Governance
Govern it, trace it, host it — roles and provenance on every dataset, and a deployment that answers to you.
Sovereign by design, not by add-on.
Permissions and provenance are attached to every dataset — not retrofitted around a public bucket.
Choose who sees and edits each layer, map and dashboard — a team, a single link, or the public web.
Open formats out at any time, on infrastructure you control — including entirely your own.
The rules travel with the data.
Set access per dataset, per map and per dashboard — and have the same rules apply to every API call against them.
Source, licence and version travel with the data, so every published map has an audit trail behind it.
Governance for the constraints you actually have.
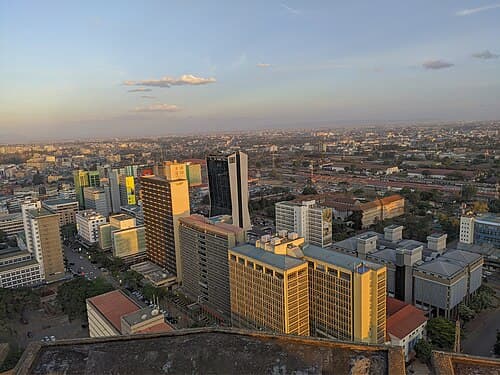
Kenya's Cloud Policy 2025 ties where government data may be hosted to how sensitive that data is, so a ministry cannot simply move its spatial layers to whichever cloud is convenient. On-premise deployment runs the whole platform — catalogue, maps, forms and dashboards — inside the ministry's own infrastructure, with hybrid reserved for the layers that are meant to be public.
Protected-area boundary plans can be shared under regulation, while poaching and patrol records are classified as restricted — and the authority's own rules forbid joining those to other data without the custodian's permission. Role-based permissions hold the restricted layers to named roles and hybrid deployment keeps them on local infrastructure, while the public map publishes from the same platform.
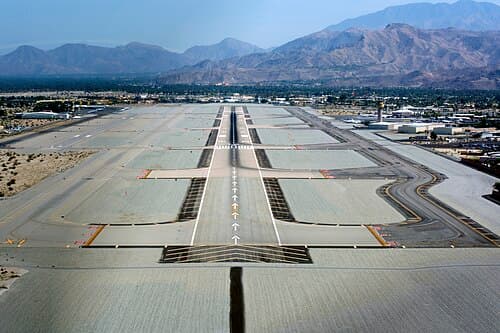
When a routing or corridor map is challenged, the agency has to state which layers it used, under what licence, and at which version each was held. Provenance travels with every dataset and the same roles apply to every API call against it, so the answer is assembled from the record rather than reconstructed from shared drives.
Questions, answered.
What does governance cover in OrionGIS?
Roles and permissions on every dataset, map and dashboard; provenance on every layer; verified AI output; and the deployment choice — OrionGIS Cloud, on-premise or hybrid — with open formats out and no lock-in by design.
Can we run OrionGIS entirely on our own infrastructure?
Yes. On-premise runs the whole platform on your own servers for complete data sovereignty — designed for government and compliance-bound organisations. Hybrid keeps sensitive data local while public-facing maps scale in the cloud.
Do we own our data?
Yes, always. Download any dataset in its original format at any time, and on-premise deployment keeps everything inside your own infrastructure. There are no per-extension licences to buy.
Ready to run it on your terms?
Talk to us about roles, provenance and deployment — cloud, on-premise or hybrid — and what your obligations require.